Summarize with:
read in < 1 min


Data center security protects physical facilities and digital assets through access controls, surveillance, and cybersecurity measures.
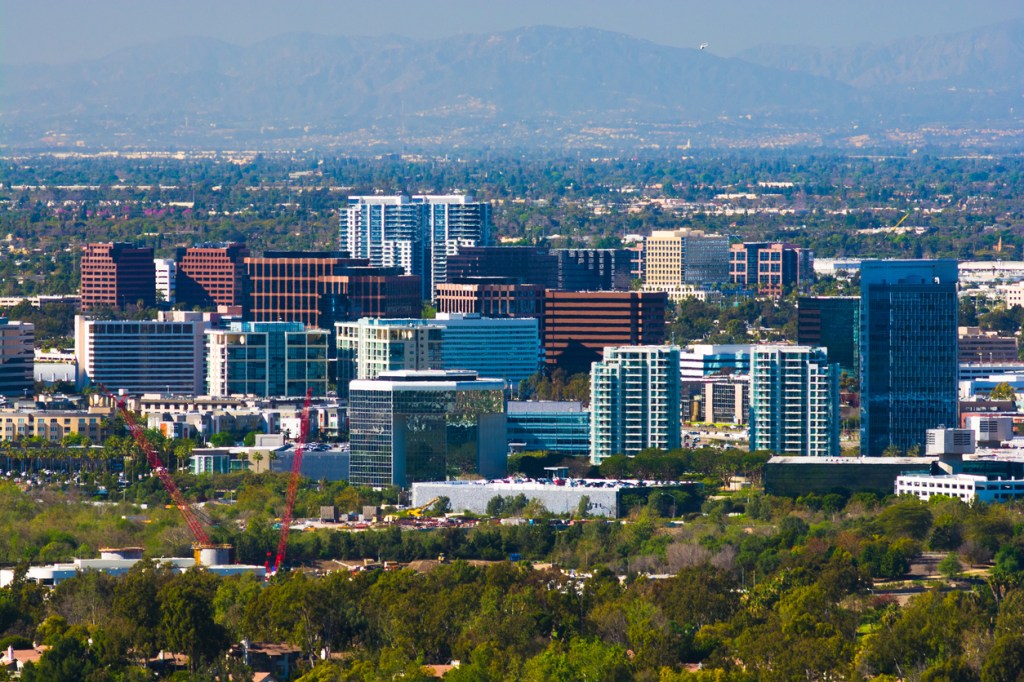
Data centers are filled with highly valuable assets, particularly data. Protecting these assets, therefore, has to be a top priority for all data center managers. With that in mind, here is a straightforward guide to the importance of security in Orange County data centers.
Why security is vital for data centers
Fundamentally, the purpose of security is to ensure the survival of a data center and its customers. Here are just five examples of what that means in practice.
Legal and regulatory compliance
Data centers store sensitive information that is subject to strict regulations such as GDPR, HIPAA, and PCI DSS. Failing to protect this data can lead to heavy fines, legal action, and loss of certifications. This means compliance is a key reason for strong security.
Ensure service availability
A security breach can disrupt a data center’s operations, causing downtime for businesses that rely on its infrastructure. Protecting data from cyberattacks ensures uninterrupted service, preventing costly disruptions for both the data center and its clients.
Prevent data loss, theft, and manipulation
Unauthorized access can lead to stolen, corrupted, or deleted data, which can have serious consequences, from financial fraud to operational failures. Implementing strong security ensures data integrity, preventing both accidental loss and deliberate tampering.
Preserve business reputation
A data breach can severely damage a company’s reputation. Organizations entrust data centers with their most valuable information, and a failure to protect it can lead to lost clients, negative publicity, and a decline in business opportunities.
Prevent financial losses
Data breaches can result in massive costs from lawsuits, regulatory fines, lost business, and the expense of remediation efforts. Strong security reduces these risks, protecting both the data center and its clients from severe financial consequences.
Key security features of Orange County data centers
The following five measures are considered to be key security features of Orange County data centers.
Multi-layered physical security
Facilities utilize 24/7 on-site security personnel, CCTV surveillance, and strict access controls. Multi-factor authentication (such as combining biometric scans and key cards) ensures only authorized personnel enter sensitive areas. Mantraps (secure entryways allowing only one person at a time) prevent unauthorized access through tailgating.
Disaster-resistant infrastructure
Disasters are both security threats in themselves and potential cover for malicious actors. Orange County has a stable climate overall, but it is in an earthquake-prone region. Data centers are therefore designed with seismic reinforcement. This prevents structural failure and so helps to ensure systems remain intact during natural disasters. There is also a minor risk of wildfires, accidental fires, and arson. This is combated by robust fire-suppression systems.
Redundant power and cooling to prevent security breaches
Backup power systems (N+1 UPS and diesel generators) and redundant cooling prevent sudden shutdowns, which could expose vulnerabilities, such as security system failures or unprotected data transfers. If power disruptions disable surveillance, access controls, or encryption tools, a facility becomes vulnerable to cyberattacks and unauthorized access. Redundant systems ensure security protocols remain active.
Network security via controlled connectivity
By offering direct access to multiple telecommunications providers in a carrier-neutral environment, data centers reduce the risk of single points of failure or network-based attacks. Private network connections minimize exposure to the public internet, reducing the likelihood of cyberattacks such as DDoS attempts or unauthorized data interception.
Compliance with security standards
Facilities adhere to strict regulatory standards such as SOC 2, HIPAA, and PCI DSS, enforcing advanced security policies, continuous monitoring, and access restrictions to protect sensitive information.
How DataBank ensures top-level security
DataBank implements a wide range of measures to ensure top-level security. Here are 7 of the most important ones.
Perimeter security
DataBank establishes strong perimeter defenses with fencing, security guards, and barriers to deter unauthorized access to the data center premises.
Surveillance systems
Advanced surveillance systems, including high-definition CCTV cameras and real-time monitoring, oversee critical areas within and around the data centers. This continuous surveillance aids in detecting and deterring unauthorized activities.
Access controls and authentication
DataBank implements stringent access controls using biometrics, key cards, and/or PINs, assigning access levels based on roles to limit entry to authorized individuals.
Environmental controls
To mitigate risks such as heat exposure and fire, DataBank maintains optimal temperature and humidity levels through robust HVAC systems and air filtration. High-efficiency air filtration systems remove airborne contaminants, improving indoor air quality and protecting equipment.
Network security
Robust network security measures are in place to protect against cyber threats. These include firewalls, intrusion detection and prevention systems, and regular security audits to identify and address vulnerabilities.
Data encryption
To safeguard sensitive information, DataBank employs robust data encryption protocols. This process converts data into a secure format that is unreadable without proper decryption keys, protecting it from unauthorized access during storage and transmission.
Compliance and data governance
DataBank ensures adherence to industry-specific and location-specific laws and regulations, such as HIPAA for healthcare or GDPR for data privacy. This provides objective proof of DataBank’s security standards.